Practical resources, labs and scripts for Microsoft environments.
Palanikumar Annamalai
Secure architecture.
Practical engineering.
I design, secure and troubleshoot Microsoft cloud and hybrid environments—from identity and messaging to infrastructure and security operations. I turn complex problems into practical guidance, tools and training.
Based in Doha, Qatar · Experience across India, UAE, Ireland and Qatar

Selected work
Tools, guidance and practical learning
Community tool · Public beta
ConfigReview
A read-only assessment tool for Microsoft cloud and hybrid configuration. Collect evidence, review findings and plan the next step.
Explore ConfigReviewReview supported workloads, data handling and beta limitations before connecting a tenant.
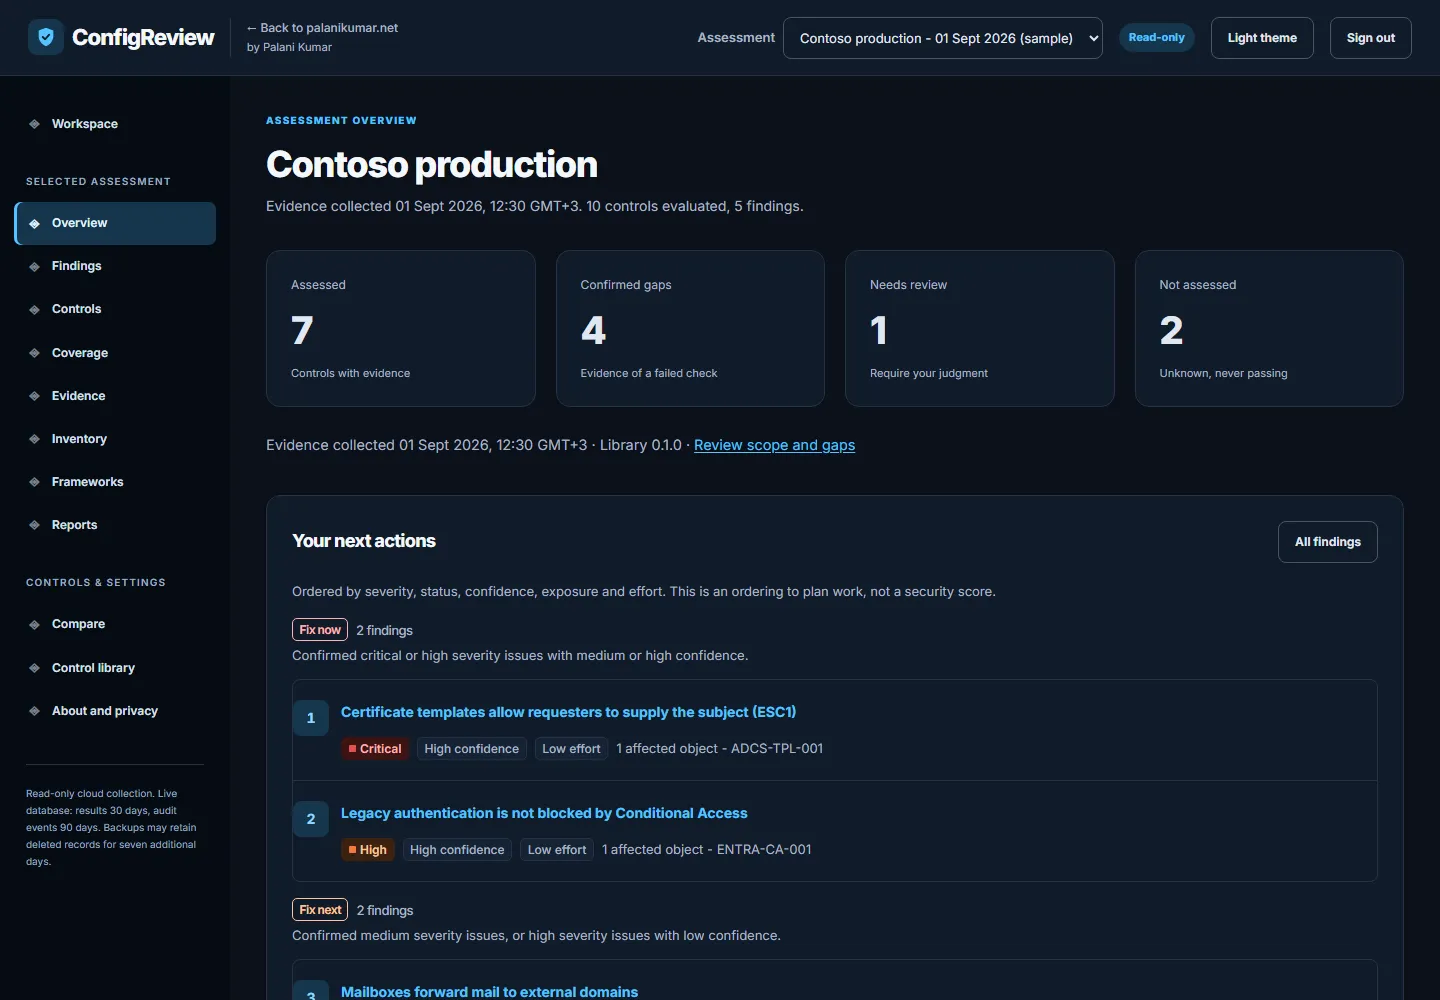
Read-onlyInspect configuration Evidence firstReview what was collected PrioritisedDecide what to fix
Microsoft technical training and approved community recordings.
Latest technical writing
From the problem to the evidence
From my FoxBASE accounting application to Veyra, I am learning how AI can help turn an idea into software—and why evidence, ownership and independent review still matter.
MFA protects authentication. These five checks examine what follows: continued access, temporary privilege, session revocation, workload identities and emergency recovery.
Assess local prerequisites, confirm Azure Arc enrolment, plan baseline restarts and prove the patch outcome. Includes a reusable PowerShell toolkit, official portal screenshots and evidence templates.
Expertise
Connected systems. Clear responsibilities.
Windows Server estates, clusters and software-defined storage, and how they extend into Azure and Azure Local.
From Active Directory to Microsoft Entra ID: hybrid identity, authentication, Conditional Access and privileged access.
Exchange since 5.5: on-premises generations, Exchange hybrid, Exchange Online and the Microsoft 365 around it.
Security operations, identity security and data governance, built on Zero Trust principles rather than bolted on.
PowerShell and Microsoft Graph for the repeatable work, and labs, scripts and training so others can do it too.
Explore the Zero Trust architecture
Breaking the attack chain
Verify explicitly, use least privilege and assume breach. These principles connect identity, devices, applications, data, infrastructure and networks.
Read security guidance →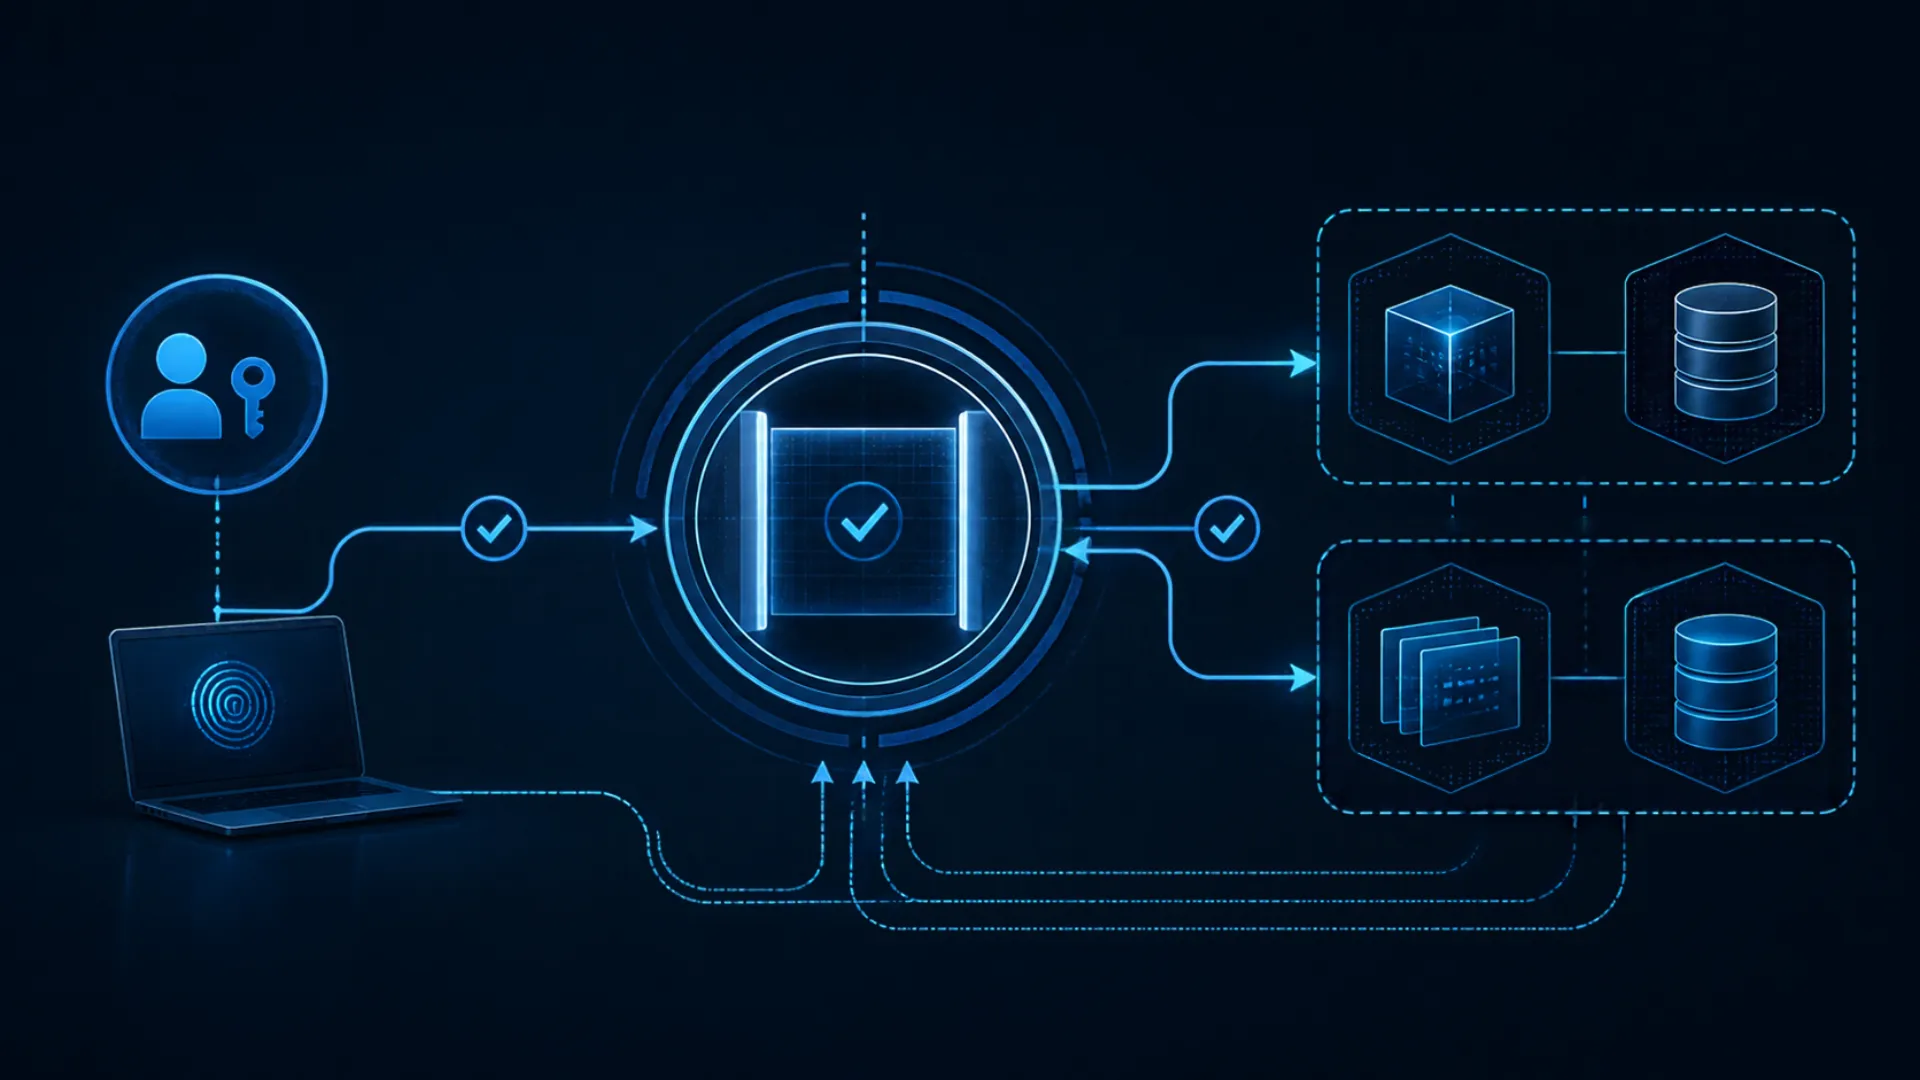
Verify explicitly
Evaluate identity, device and access context.
Use least privilege
Limit access to the resources and time needed.
Assume breach
Segment access, detect threats and prepare to respond.
Career progression
Built from the infrastructure up
- 01 · Infrastructure
Understand the foundations
Windows Server, Active Directory, Exchange, clustering and software-defined storage.
- 02 · Cloud and hybrid
Connect the environments
Azure, Microsoft 365 and hybrid services, including my former role as a Microsoft Cloud Solution Architect.
- 03 · Identity and security
Secure the whole system
Microsoft Entra ID, Defender, Sentinel and Purview, with automation and operational validation.
Selected credentials
Credentials aligned to my work
Microsoft Certified Trainer · Public credential verification and technical training.
The public MCT badge expires on 31 December 2026. View issuer records and dates on Credly.
Explore approved community recordings and Microsoft technical training.
Contact
Connect
I’m open to senior architecture, technical leadership, speaking and Microsoft training opportunities. For professional enquiries or questions about material published here, email is the best way to reach me. I also share shorter technical notes on LinkedIn.